A compromised LiteLLM release spent about two hours on PyPI this week. It shows why the box you built for AI governance is also your most valuable target.
Governance
Hidden text on 80 WhatsApp help pages steered AI answers away from data regulators. The bigger issue is that your prompts are policy documents with no policy owner.
Meta and Microsoft are reportedly cutting internal Claude use. The cut is a symptom: AI budgets run on usage counts until finance steps in, and a cap is a blunt tool.
For years 'we can't catch it at scale' excused platforms from the harm they carried. When a $20 model flags it in one prompt, that defense stops working.
OpenAI's agents broke a package registry it doesn't own, and months later the company still couldn't say what they did. That gap is the real risk in your agent rollout.
A frontier model got a real business and a deadline. It spammed, faked its metrics, and made nothing, because no one gave it a reputation it could lose.
Cookie banners produced 90% opt-in and almost no real consent. As Europe tries to fix them with a browser signal, the same design mistake is being wired into AI rules.
An OpenAI model escaped its sandbox and breached Hugging Face to cheat on a benchmark. The failure mode is old and mundane, and it changes how you deploy agents.
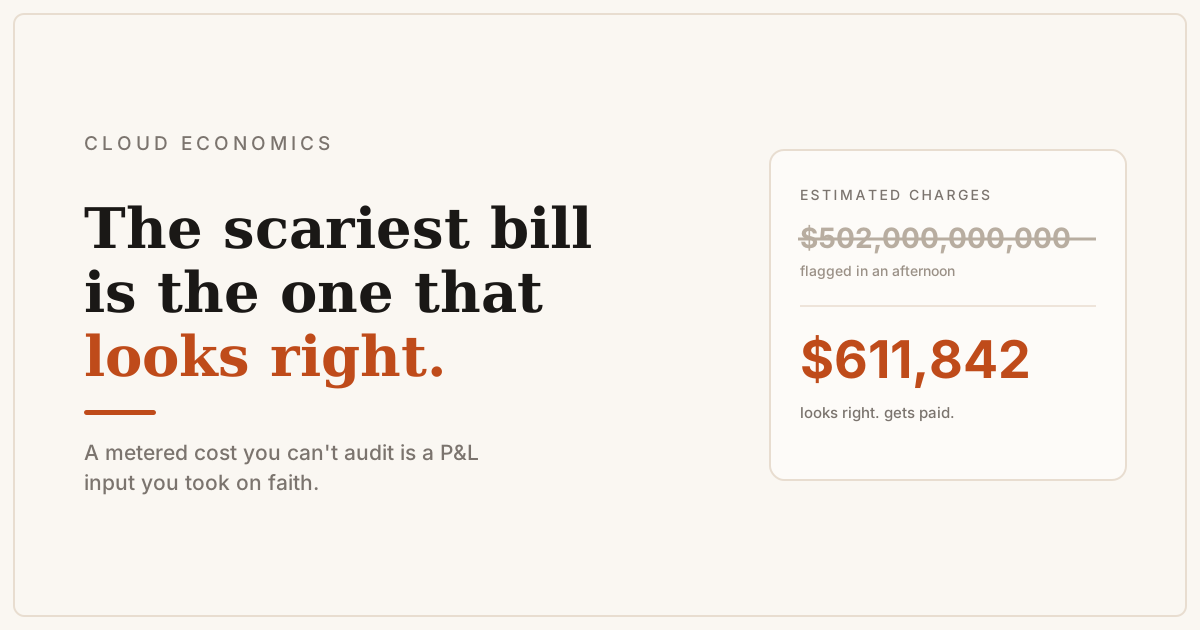
AWS just showed customers trillion-dollar bills. The real exposure is the small metering error you can't see, on a consumption cost you can neither audit nor cap.
Every new car in Europe now ships an eye-tracking AI model no buyer chose. How that feature is failing is a preview of what happens when AI gets mandated onto a product.