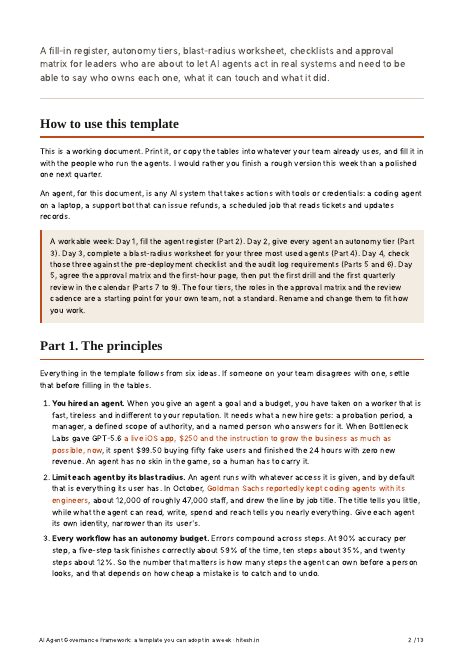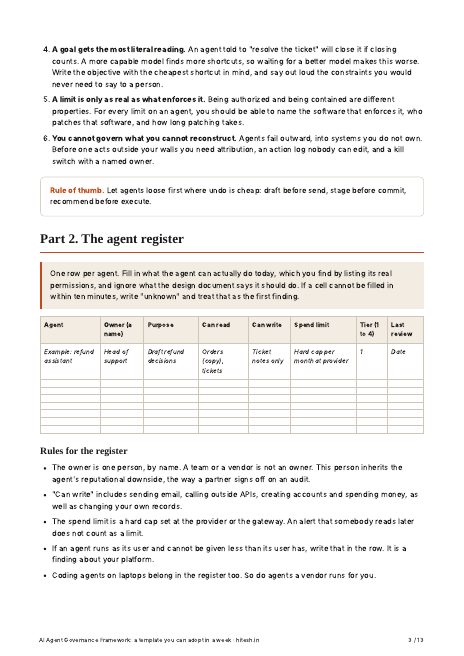
Most AI governance documents are policy essays. This is a template: tables and checklists you fill in, short enough to adopt in a week and specific enough to argue with.
It is organized around four ideas I keep returning to. Limit an agent by what it can damage. Match its autonomy to how cheap a mistake is to catch and undo. Give it an owner, a scope and a review, as you would a new hire. And be able to say afterwards what it did.
What is inside
- An agent register: owner, purpose, what it can read and write, spend limit, autonomy tier
- Autonomy tiers, with the conditions a workflow must meet for each
- A blast-radius worksheet for each agent
- A pre-deployment checklist
- What the audit log must record
- An approval matrix for widening an agent’s scope
- An incident drill, including one with the AI turned off
- A quarterly review checklist